Deaf by Design: How AV Companies Built a System That Ignores You On Purpose
Photo: Erik Calonius, Public domain, via Wikimedia Commons
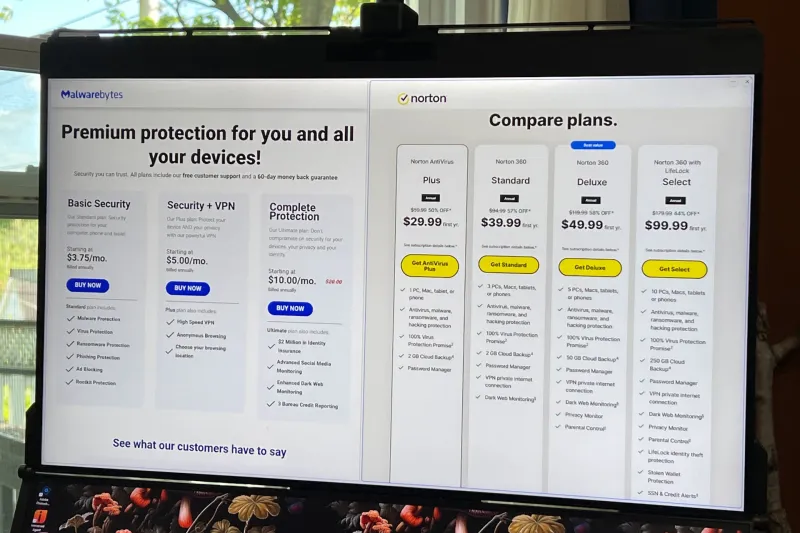
Here's a scenario that probably sounds familiar to at least a few of you in the NoDAVG community. You're running one of the big-name antivirus suites — the kind with the splashy commercials and the five-star review badges plastered all over their homepage — and something goes sideways. Maybe it's flagging your accounting software as malware. Maybe it missed something that clearly should have triggered an alert. You dutifully fill out the feedback form, attach the logs, write a polite but detailed description, and hit submit.
Then you wait.
And wait.
And eventually, you stop waiting, because the silence makes it pretty clear that nobody on the other end was ever really listening.
This isn't a one-off customer service failure. It's a pattern — and once you understand the business logic underneath it, the silence starts to make a lot more sense.
The Feedback Loop That Doesn't Loop Back
Most major AV vendors maintain some version of a user submission portal. Norton has one. McAfee has one. Bitdefender, Malwarebytes, Trend Micro — they all do. On paper, these portals are supposed to function as a direct line between the people using the product in the real world and the threat intelligence teams that update detection databases.
In practice, they're closer to a suggestion box bolted to the wall of a very busy office where nobody checks the box.
The structural problem is this: the teams that handle user submissions are almost never the same teams that get credit for improving detection rates. Threat intelligence is a prestige function inside these companies. It's where the researchers with conference talks and published papers sit. User-submitted false positives and missed detections? That's triage work. It's reactive, it's unglamorous, and in most org charts, it sits several rungs below the people building the headline features.
When resources get allocated — and they always get allocated based on what moves the needle on marketing metrics — the submission queue loses. Every time.
Detection Rate Theater Has a Villain, and It's Incentives
Here's where it gets a little cynical, but bear with us.
AV vendors live and die by their scores on third-party testing platforms like AV-TEST and AV-Comparatives. These benchmarks measure detection rates under controlled lab conditions using known malware samples. A 99.7% detection rate looks incredible on a box. It's the kind of number that closes sales.
What those benchmarks don't measure is how quickly a vendor responds when a legitimate piece of software gets incorrectly nuked, or how a product performs when a customer reports a novel threat variant that slipped through. There's no quarterly ranking for "responsiveness to user-reported issues." There's no badge for "actually fixed the thing you complained about."
So vendors optimize for what gets measured. They pour engineering resources into the detection pipelines that feed the benchmark scores, and they treat the user feedback channel as a compliance checkbox rather than a genuine intelligence source. The incentive structure doesn't just tolerate this — it actively rewards it.
The False Positive Problem Nobody Wants to Own
False positives are a particularly sore spot. When an antivirus incorrectly flags a clean file as malicious, the consequences can range from annoying to genuinely destructive. Small businesses have had legitimate software quarantined mid-operation. Developers have lost hours of work when build tools got wiped. Home users have had family photos flagged as suspicious and moved to quarantine folders they didn't know existed.
When these users report the issue, the standard response — if there is one — tends to follow a predictable script. You'll get an automated acknowledgment. Maybe a form letter asking for additional files. Then, more often than not, a wall of silence or a generic closure notice weeks later with no explanation of what, if anything, changed.
The vendors that do respond with any speed tend to be the smaller, more community-adjacent players. But even then, the fix rarely comes with any transparency about what went wrong or how the detection logic is being updated to prevent recurrence. The user who reported the issue almost never finds out whether their report actually contributed to anything.
Who's Actually Filling the Gap
This is where the NoDAVG community angle gets genuinely interesting, because the accountability vacuum left by commercial vendors hasn't gone unfilled — it's just been filled by people outside the traditional AV industry.
Open-source projects like ClamAV have built community-driven signature databases where contributors can actually see the logic behind detections and submit pull requests to fix bad rules. Platforms like VirusTotal, while not a traditional AV product, have become de facto community forums for analyzing suspicious files and cross-referencing detections across dozens of engines simultaneously.
Forum communities — Reddit's r/antivirus, Wilders Security, and yes, spaces like this one — have become the real first-line triage for users who can't get answers from vendors. Experienced community members often diagnose false positives faster than official support channels, and the institutional knowledge built up in these spaces is genuinely impressive.
There's also a growing movement around threat intelligence sharing platforms that operate outside the vendor ecosystem entirely. ISACs (Information Sharing and Analysis Centers), open threat feeds, and community-curated blocklists are all filling roles that commercial AV vendors have largely abdicated when it comes to real-world user responsiveness.
What Would Actually Fix This
Honestly? A few things would help, and none of them require a complete industry overhaul.
First, third-party benchmarking organizations could add responsiveness metrics to their evaluations. How long does a vendor take to remediate a confirmed false positive after user submission? Is there a public-facing status tracker for reported issues? These are measurable things, and measuring them would change vendor behavior almost immediately.
Second, vendors could publish aggregate data on their submission queues — how many reports come in, how many get acted on, average resolution time. Right now, this data is treated as proprietary. There's no good reason for that other than the fact that the numbers would probably be embarrassing.
Third — and this is the one that probably won't happen without regulatory pressure — there could be mandatory disclosure requirements for significant false positive events, similar to how data breaches have to be disclosed. If an AV update incorrectly quarantines system files on a hundred thousand machines, that's a material event. Users deserve to know about it.
The Takeaway
The antivirus industry has built an extraordinarily effective marketing apparatus around the idea of protection. The imagery, the language, the benchmark scores — all of it communicates vigilance and responsiveness. But the internal structure of most commercial AV companies is optimized for something much narrower: looking good on the metrics that drive sales.
Your feedback, your false positive reports, your missed detection logs — these are, at best, a secondary concern. At worst, they're a liability that gets managed rather than addressed.
The good news is that the community has noticed. And in a lot of ways, the community is doing a better job of holding these vendors accountable than the vendors' own internal processes ever have. That's not nothing. But it probably shouldn't be the whole answer.